by Josef Weiss
CISA issued Binding Operational Directive (BOD) 26-04 to update the previous BOD version 22-01, Reducing the Significant Risk of Known Exploited Vulnerabilities establishing a CISA managed catalog of known exploited vulnerabilities and requires federal civilian agencies to identify and remediate these vulnerabilities on their information systems. Tenable.sc allows organizations to quickly summarize and track specific vulnerabilities to ensure proper discovery and mitigation. This report showcases progress in mitigation of these vulnerabilities to allow organizations to ensure a reduced attack surface.
The Directive was updated for two reasons: The first is the deteriorating effectiveness of traditional vulnerability management. Citing the 2026 Verizon Data Breach Investigations Report, CISA’s blog post accompanying the directive notes that only 26% of KEV-listed vulnerabilities were fully remediated by organizations in 2025, a decline from 38% the previous year. Meanwhile, the median time to fully resolve vulnerabilities rose to 43 days. In an environment where exploitation can occur within hours of disclosure, the remediation gap is widening.
The second factor is artificial intelligence. CISA explicitly states that AI is accelerating both vulnerability discovery and weaponization, narrowing the window of time that exists between vulnerability disclosure and exploitation.
Directive 26-04, Reducing the Significant Risk of Known Exploited Vulnerabilities establishes a CISA-managed catalog of known exploited vulnerabilities that carry significant risk to the federal enterprise and establishes requirements for agencies to remediate any such vulnerabilities included in the catalog. CISA will determine vulnerabilities warranting inclusion in the catalog based on reliable evidence that the exploit is being actively used to exploit public or private organizations by a threat actor.
Tenable.sc uses active credentialed scanning and/or agent based scanning to collect information needed to identify known exploitable vulnerabilities. Allowing the risk manager to work with asset owners to establish an ongoing remediation action plan, which demonstrate compliance with this directive.
Chapters
Executive Summary - This chapter contains a number of widgets designed to provide a quick overview and status of the BOD Program.
BOD 26-04 Assets with an Active KEV - This chapter lists the assets carrying CISA known exploited vulnerabilities. Assets are ordered by risk score; only the top 10 are expanded with detail pages.
BOD 26-04 - Vulnerability Summary for CISA Known Exploited Vulnerabilities - This chapter summarizes known exploited vulnerabilities by plugin. The detail pages shows plugins ordered by severity, with affected assets and plugin output.
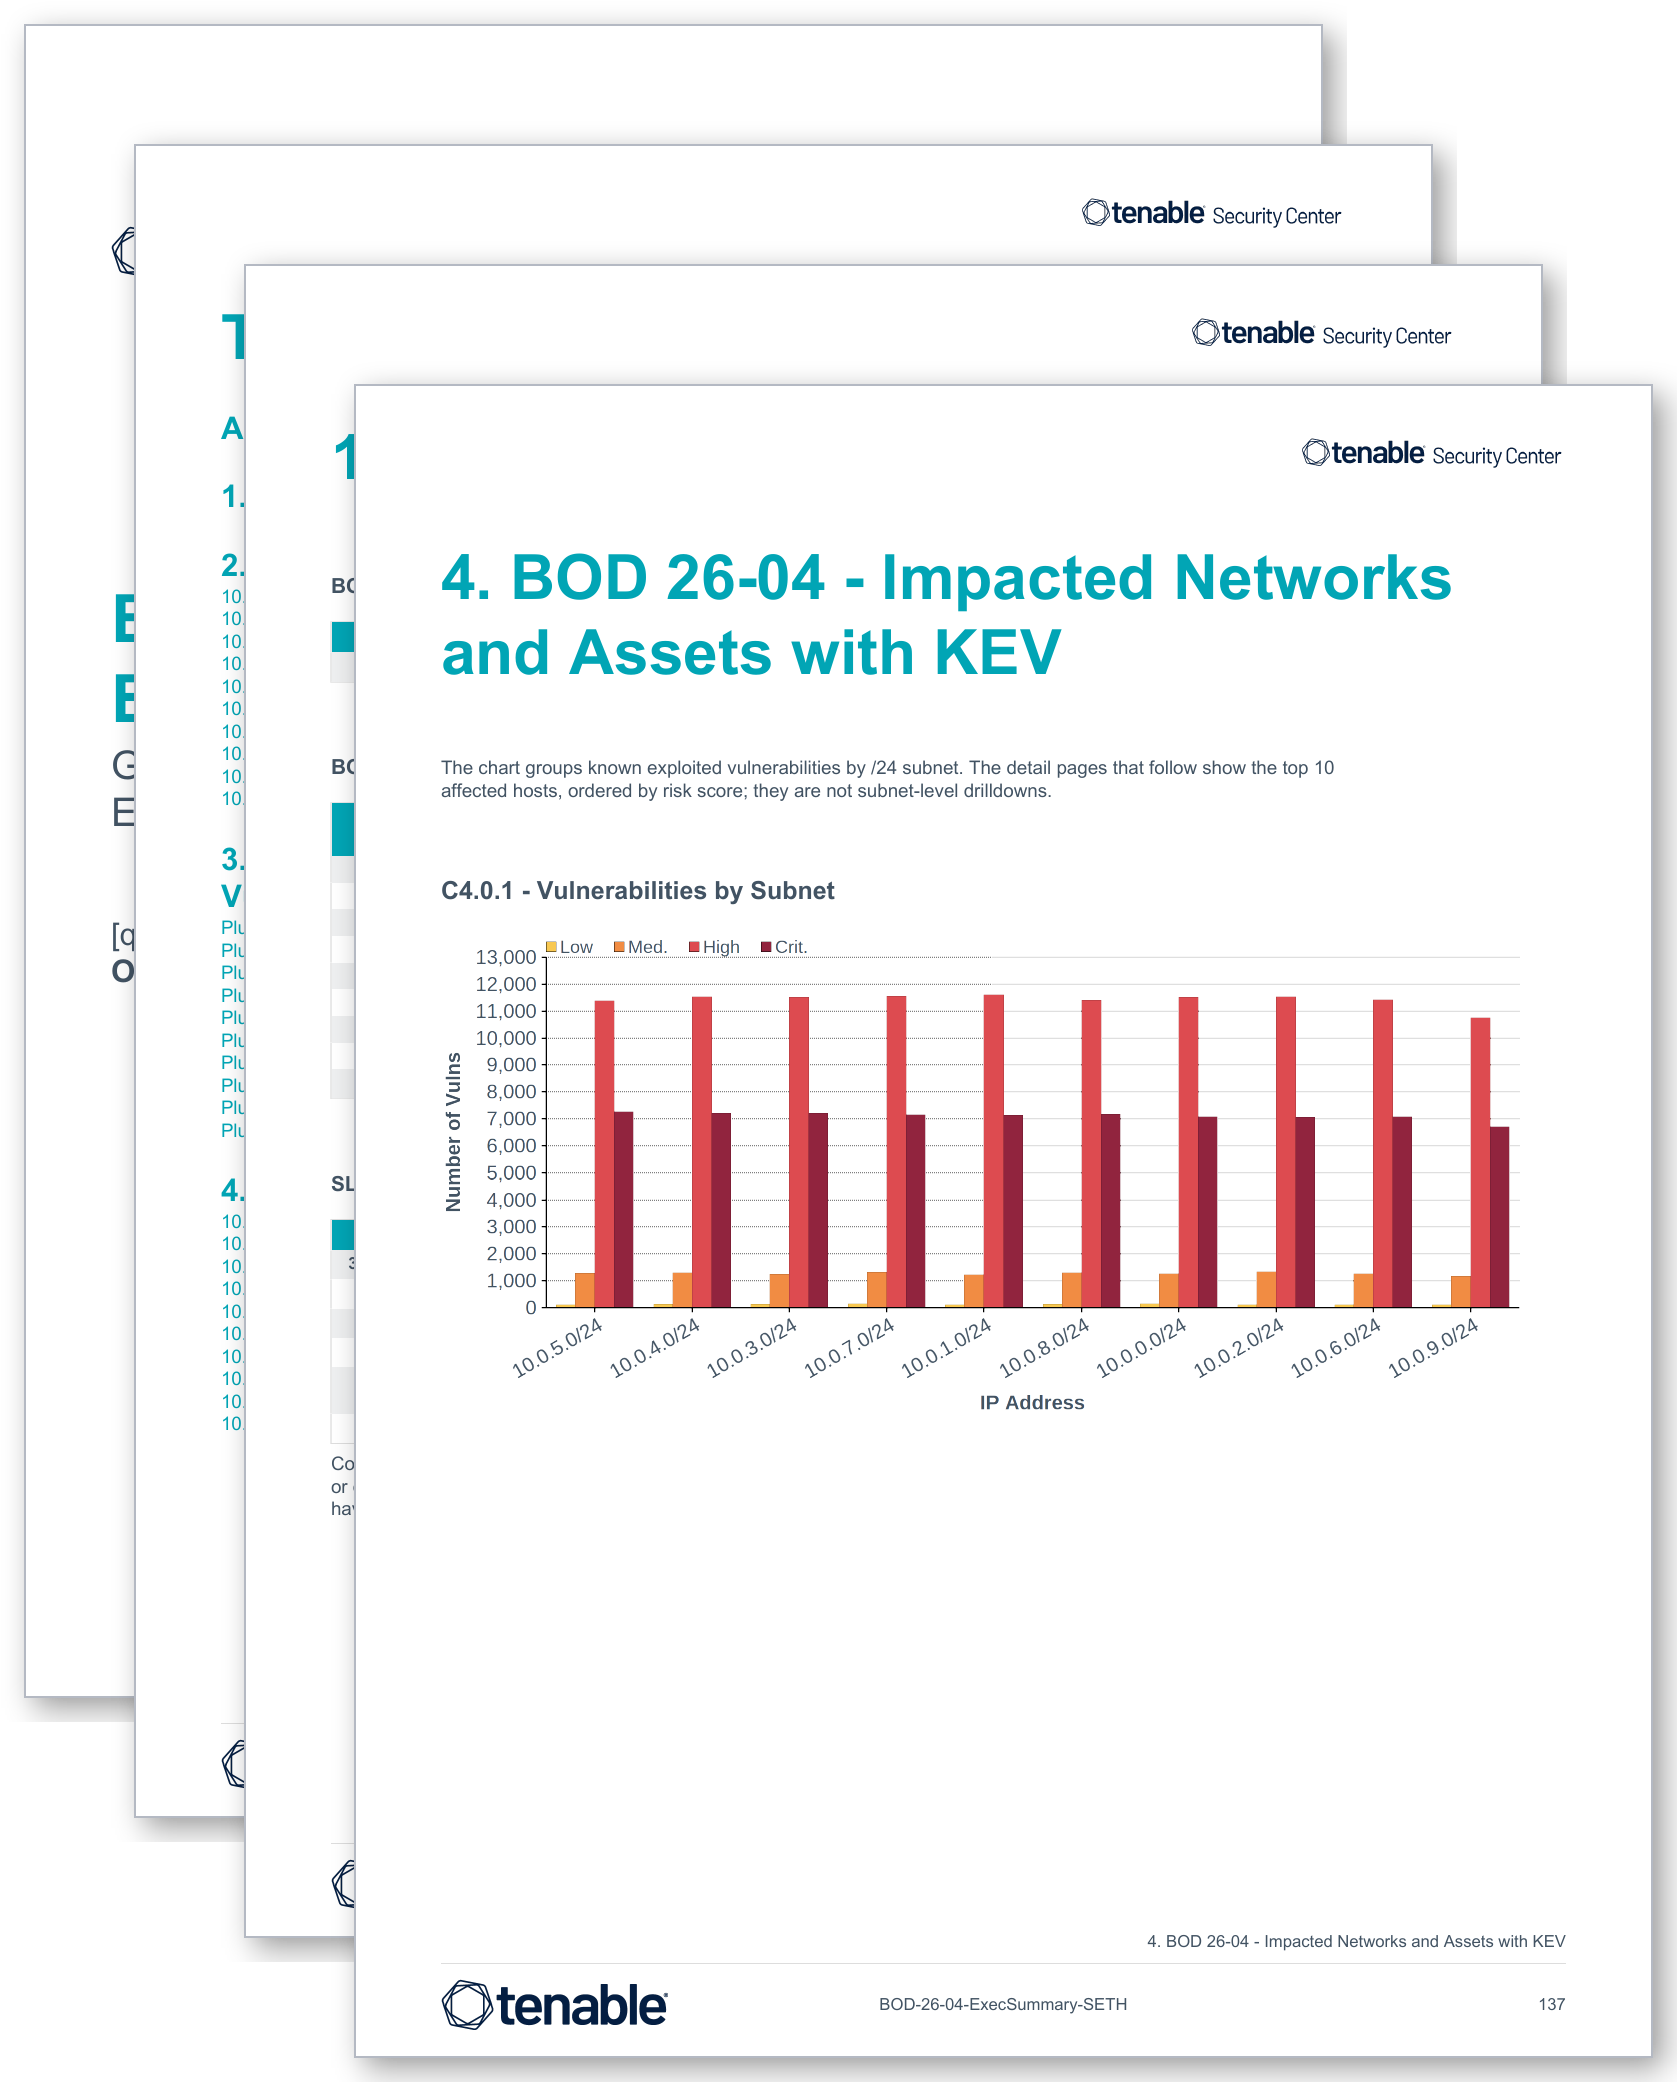
BOD 26-04 - Impacted Networks and Assets with KEV - This chapter groups known exploited vulnerabilities by /24 subnet. The detail pages that follow show the top affected hosts, ordered by risk score; they are not subnet-level drilldowns.
Tenable One
Request a demo
The world’s leading AI-powered exposure management platform.
Thank You
Thank you for your interest in Tenable One.
A representative will be in touch soon.
Form ID: 7469
Form Name: one-eval
Form Class: c-form form-panel__global-form c-form--mkto js-mkto-no-css js-form-hanging-label c-form--hide-comments
Form Wrapper ID: one-eval-form-wrapper
Confirmation Class: one-eval-confirmform-modal
Simulate Success